
Wp.com: Protection Against Brute-Force Attacks on WordPress
A layered defense approach to protect wp-login.php and XML-RPC from brute-force attacks, using server configuration, WAF rules, and lightweight PHP code.

A layered defense approach to protect wp-login.php and XML-RPC from brute-force attacks, using server configuration, WAF rules, and lightweight PHP code.
Advanced WordPress Security Vulnerabilities: Exposed Debugging, Insecure Permissions, REST API, HTTP Headers, JWT, Unencrypted Copies, and Unprotected Logs. Includes a review checklist.
The Most Common Security Issues in WordPress and How to Fix Them: Weak Passwords, Outdated Software, Insecure Permissions, Backups, XML-RPC, and wp-cron.
How to Use WP-CLI to Audit and Strengthen WordPress Security: Detect Outdated Components, Verify Integrity, Harden Settings, and Automate Checks.
On October 9, 2025, my article “Security Threats in WordPress: Detection, Cleanup, and Prevention” was published on the Spanish-language WordPress.com blog. I approach security as a process of detection, cleanup, and prevention to identify a compromised site, act quickly, and reduce the likelihood of the problem recurring. It covers the most common threats and maintenance …
El 27 de agosto de 2025 se publicó en el blog en español de WordPress.com mi artículo Gestión avanzada de usuarios, roles y permisos en WordPress. Explico cómo organizar usuarios, roles y capacidades con el principio de mínimo privilegio para evitar accesos innecesarios, errores humanos y riesgos de seguridad. El artículo incluye la gestión en …
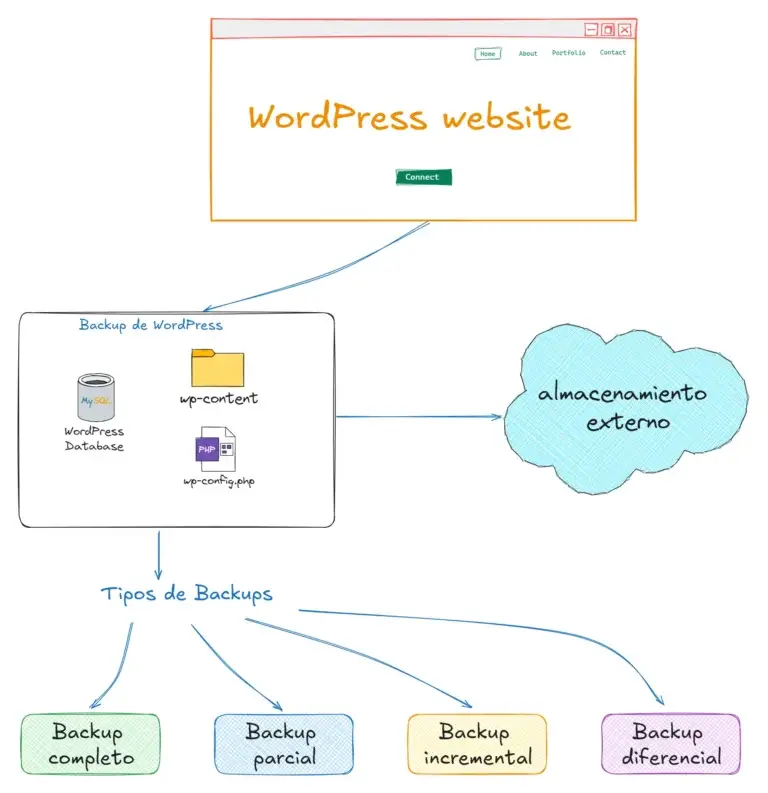
WordPress backups: advanced options, partial restores. is a long article of about 25 minutes of reading time.
I recently had the honor of boarding A Ticket to Chattanooga with Ana Cirujano and Pablo Moratinos who have driven this locomotive beautifully.
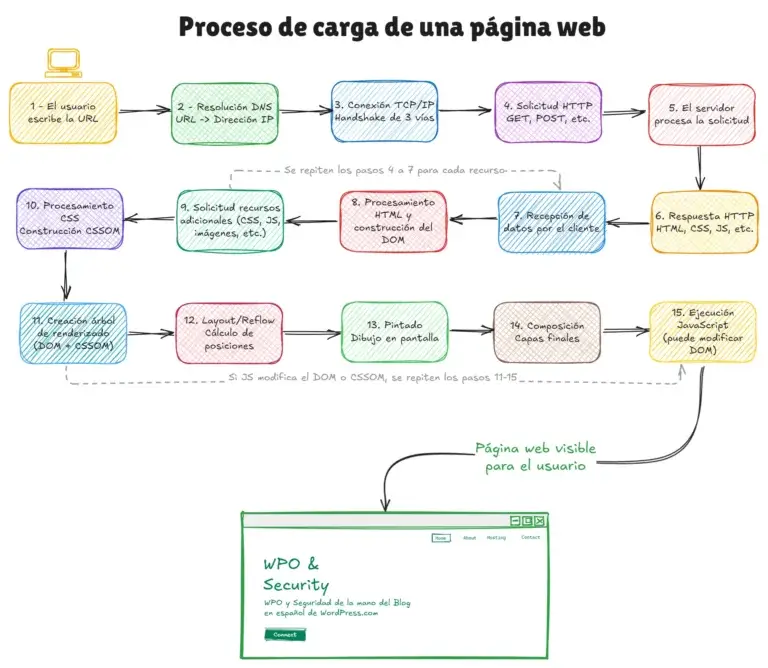
My article Complete WordPress Security from DNS to Browser has been published in the WordPress.com Spanish Blog.